
The movement represents 2.8% of the total exploit funds tracked by Galaxy Digital. According to head of research Alex Thorn, the Bitcoin originated from specific exploit clusters labeled AA, AU, and AX. The transaction included an OP_RETURN message directing claimants to the Crypto Recovery Trust, a statutory entity managed by Agentic Trace LLC that handles ownership verification and sanctions screening.
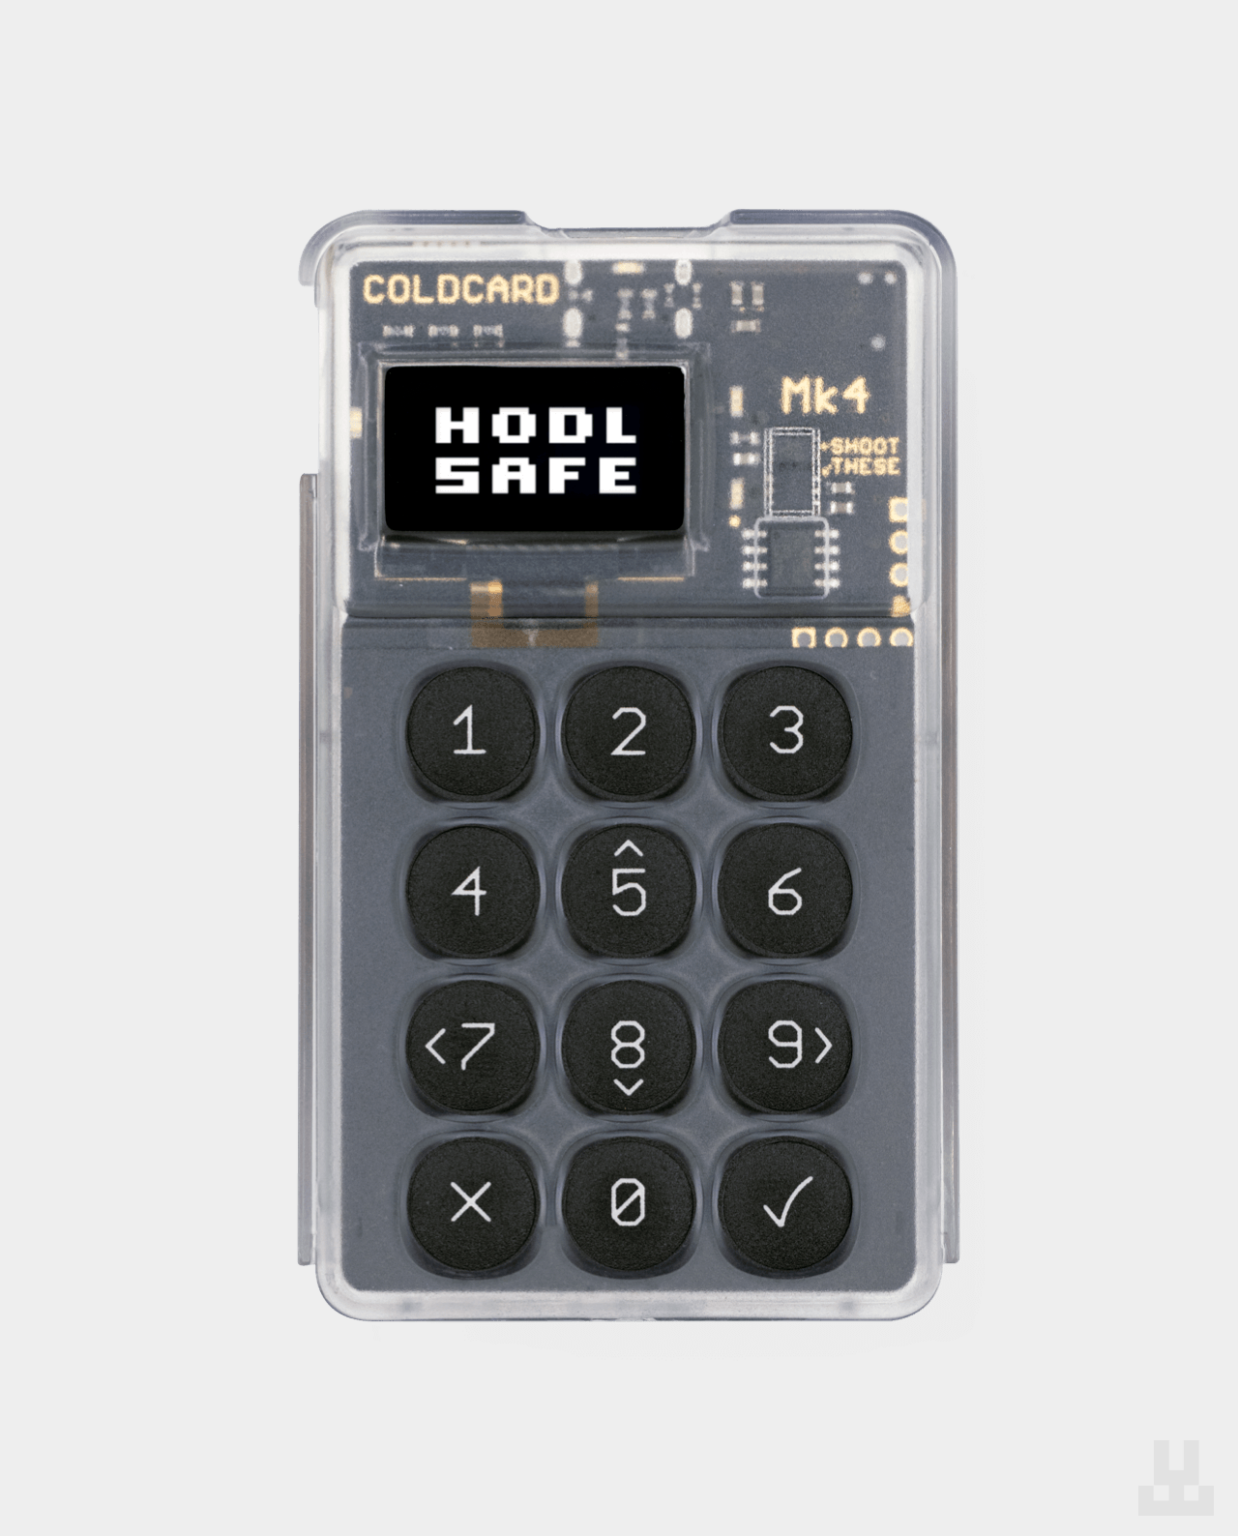
This consolidation follows earlier efforts by the Digital Asset Recovery Trust (DART), which had previously secured over 50 BTC to prevent malicious actors from accessing vulnerable addresses. While these recovery efforts provide a path for victims, manufacturer Coinkite maintains that patching firmware cannot retroactively secure seeds generated during the initial exploit period. Users remain at risk if they continue to rely on seeds created under the flawed firmware, which suffered from reduced entropy due to a pseudorandom generator error. Coinkite advises all affected users to generate new, secure seeds and migrate their funds immediately, noting that only a manual entropy process, such as independent dice rolls, can supplement a potentially weakened wallet seed.
Comments (0)
No comments yet. Be the first!